What Is a Merkle Allowlist? How NFT Mints Verify Your Spot
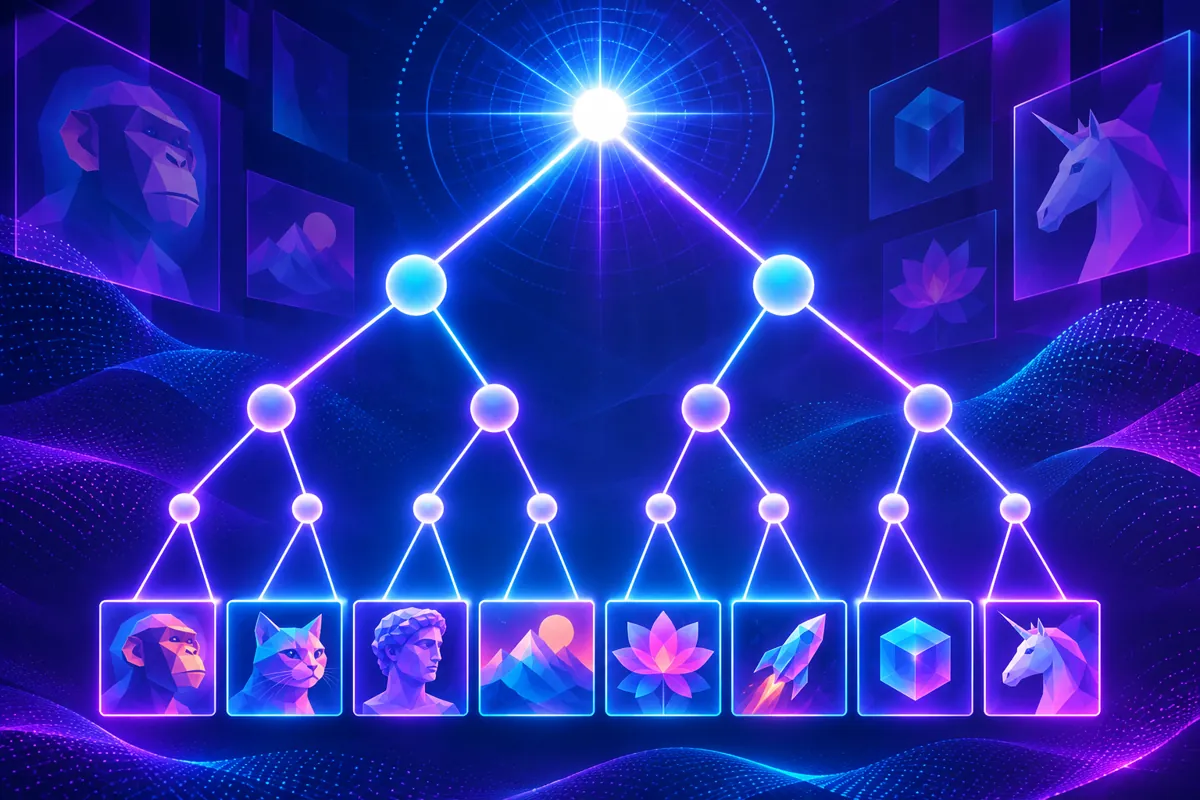
Table of Contents
If you have ever joined an allowlist for an NFT drop and then watched a mint transaction succeed in seconds, a Merkle tree was probably doing the quiet work behind it. It is one of the more clever pieces of cryptography used in NFT minting, and understanding it makes allowlist mints, and the occasional failed one, much easier to reason about.
The problem a Merkle tree solves
Imagine a collection with ten thousand allowlist spots. A smart contract could, in theory, store every eligible wallet address directly on chain and check new mints against that list. It would work, but it would be expensive. Writing thousands of addresses to a contract costs gas for every single one, and that cost is paid once by the project and then again every time the list needs to change.
A Merkle tree avoids that by compressing the entire list into a single, fixed size value called a root hash. The contract stores only that one hash, no matter how many addresses are on the list. The actual addresses, and the proof that a given wallet belongs on the list, are kept off chain and handed to the contract only at the moment someone mints.
How the tree is built
The process starts with the full allowlist, sometimes paired with a per wallet mint limit. Each entry is hashed into what is called a leaf. Pairs of leaves are then hashed together to form the next layer up, and that pairing repeats, layer by layer, until a single hash remains at the top. That final hash is the Merkle root, and it is the only piece of the list that ever gets written to the smart contract.
Because every layer depends on the one below it, changing even one address in the list produces a completely different root. That property is what makes the root trustworthy as a stand in for the whole list.
What happens when you mint
When an allowlisted wallet tries to mint, it does not send the whole list to the contract. It sends its own address, sometimes its allowed quantity, and a short set of hashes called a Merkle proof, essentially the specific path from that wallet’s leaf up to the root. Minting tools and front ends generate this proof automatically, so the person minting does not see or handle it directly.
The contract then recomputes the hash path using the submitted proof and compares the result against the root it already has stored. If the two match, the wallet is confirmed as part of the original list and the mint proceeds. If they do not match, because the wallet was never on the list, or the proof was altered, the transaction reverts with an error along the lines of invalid proof.
This is also why a Merkle allowlist check alone does not stop someone from minting twice. The proof confirms list membership, not whether that wallet has already claimed its spot. Contracts handle that separately, usually with a simple record that marks an address as claimed once it successfully mints.
Why projects prefer this method
- Lower gas costs. Verifying a proof costs roughly the same small amount of gas no matter how large the allowlist is, since the contract only ever compares hashes.
- Privacy for the list. The full set of allowlisted addresses is not published on chain in a way anyone can simply read from the contract. Only wallets with a valid proof can demonstrate membership.
- Flexibility before mint day. Because the list lives off chain until the root is set, project teams can add or remove wallets right up until the point they publish the root, without touching the contract code itself.
What this means if your mint fails
If an allowlist mint rejects your wallet, a few ordinary explanations are more likely than anything suspicious. The project may be using a different wallet address than the one you registered with. The proof your minting tool fetched may be stale if the list was updated after it was generated. Or the allowlist window may have simply closed before your transaction confirmed. Double checking the exact wallet address tied to your allowlist entry resolves most of these cases.
It is also worth knowing that a Merkle proof is not a secret in the way a password is. It only proves membership in a specific list for a specific contract, and on its own it cannot be used to drain a wallet or mint on someone else’s behalf. The real risks around minting still come from connecting your wallet to unfamiliar sites or approving transactions you have not read carefully, not from how the allowlist itself is verified.
The takeaway
A Merkle allowlist is ultimately a way to make a yes or no question, is this wallet on the list, cheap and verifiable without exposing the whole list or burdening the contract with its full weight. It is one of many small engineering decisions that make modern NFT drops run smoothly, even when thousands of people are trying to mint in the same few minutes.
If you are creating and minting your own NFTs rather than joining someone else’s drop, you likely will not need to build a Merkle tree by hand. The Simple NFT Creator app handles the underlying minting mechanics for you, so you can focus on the artwork and the collection itself. It is available on the App Store and Google Play.